Security Woven in Every Decision, Integrated Across Your Tech Strategy
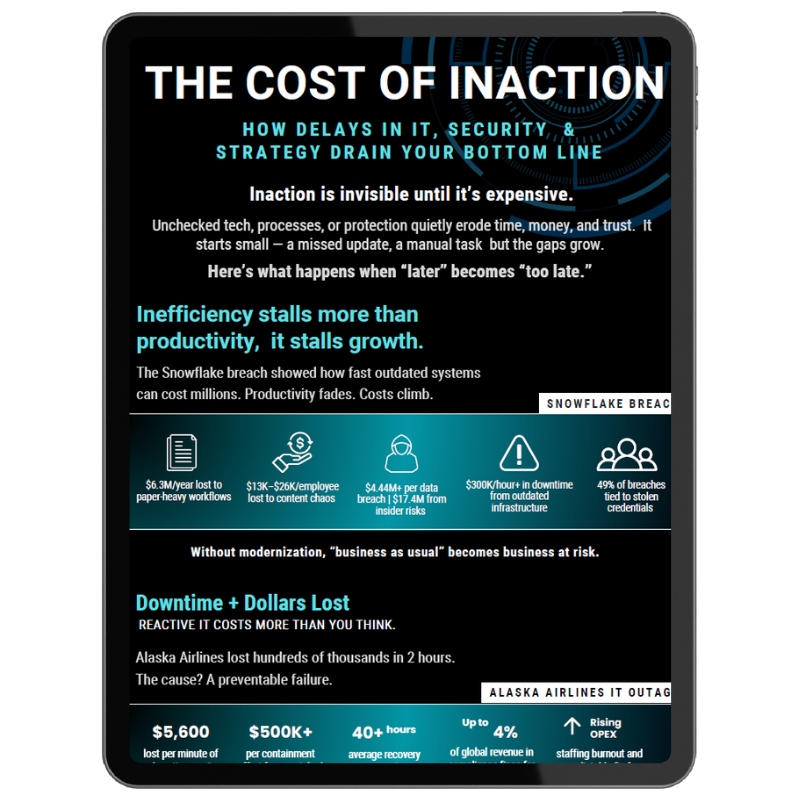
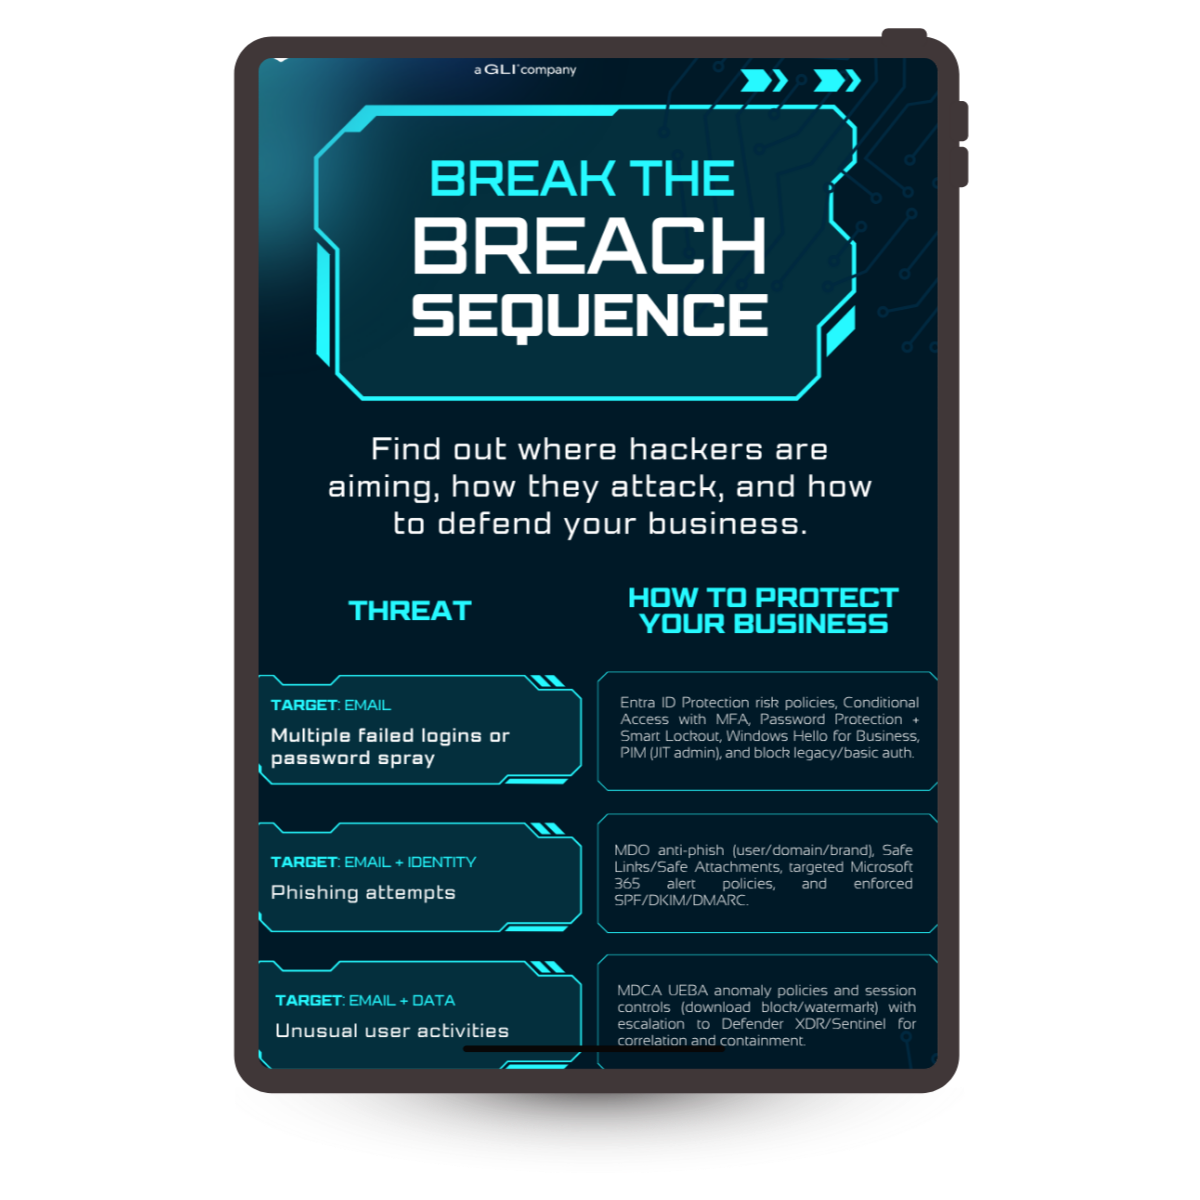
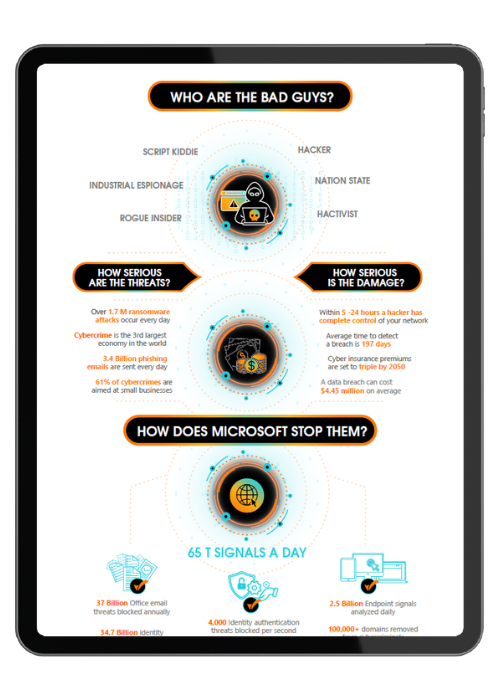
Today, the average security breach costs $4.4 million. Investigating alerts and monitoring more systems isn’t a strategy, it’s a liability.
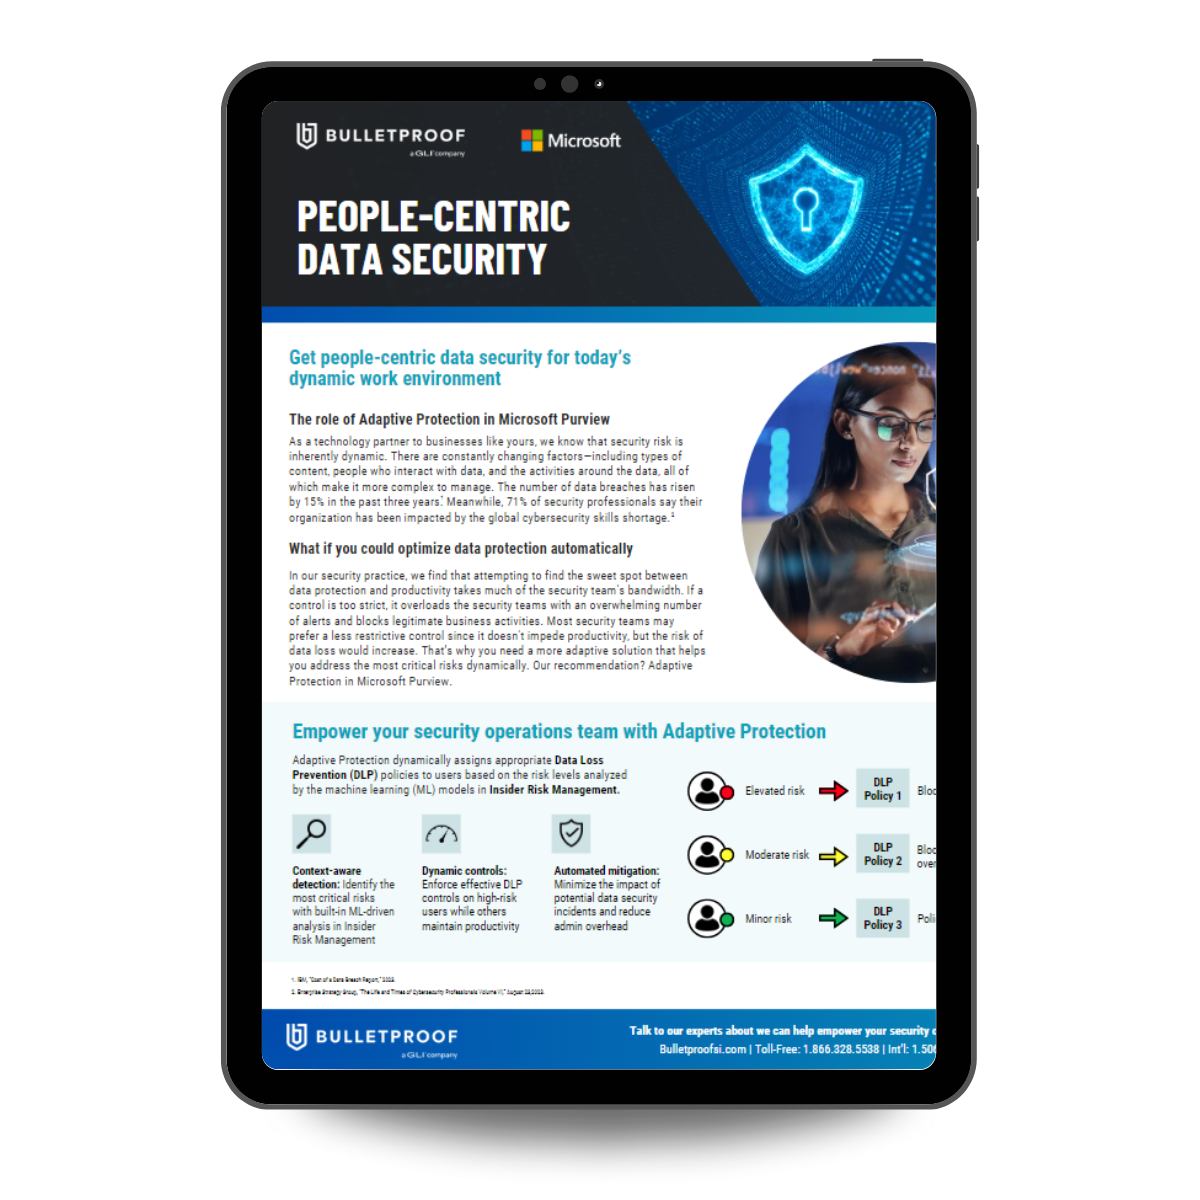
As an AI-ready managed security service provider (MSSP), we connect your entire landscape, ensuring your organization is resilient, compliant, and ready to respond to modern cyber threats.
Cut the Noise and Catch the Threats
A Better Way to Manage Security
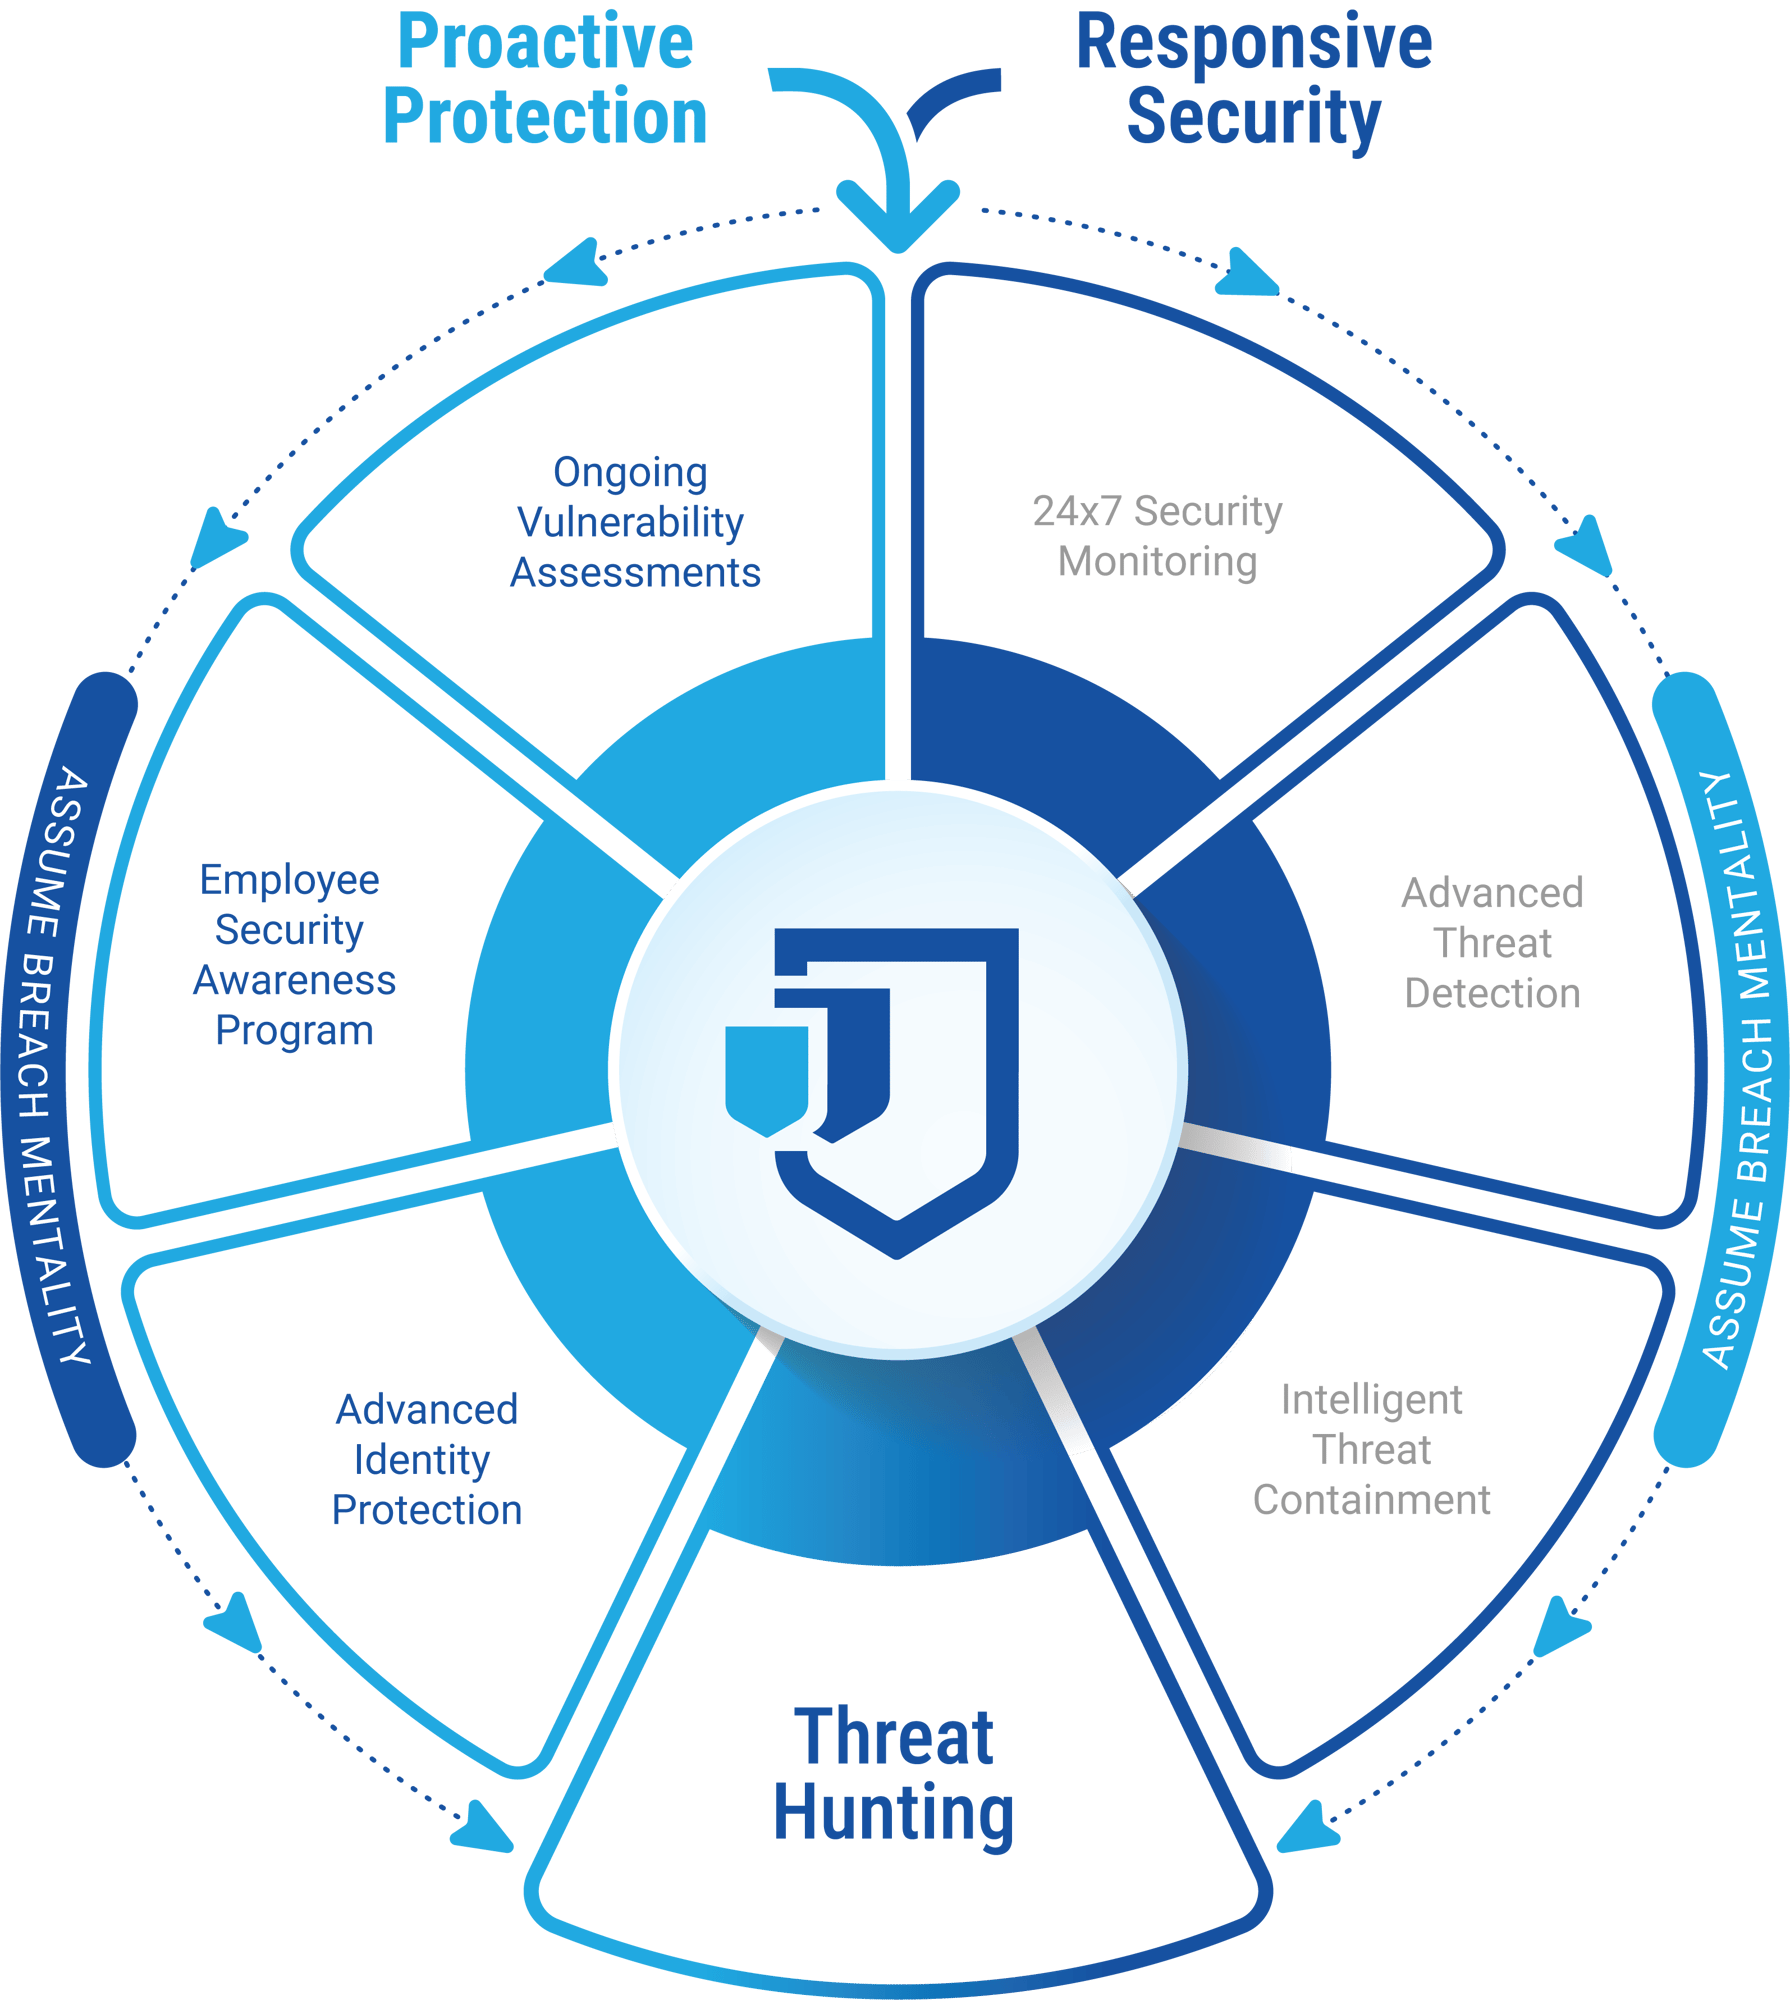
We combine strategic guidance, managed security operations, technical optimization, and incident support. Instead of managing disconnected vendors and tools, you gain a coordinated, credentialed MSSP focused on measurable risk reduction.
Get continuous protection from a geo-diverse, SOC 2 Type II-certified security operations team.
- 24/7 threat monitoring, triage, investigation, and escalation
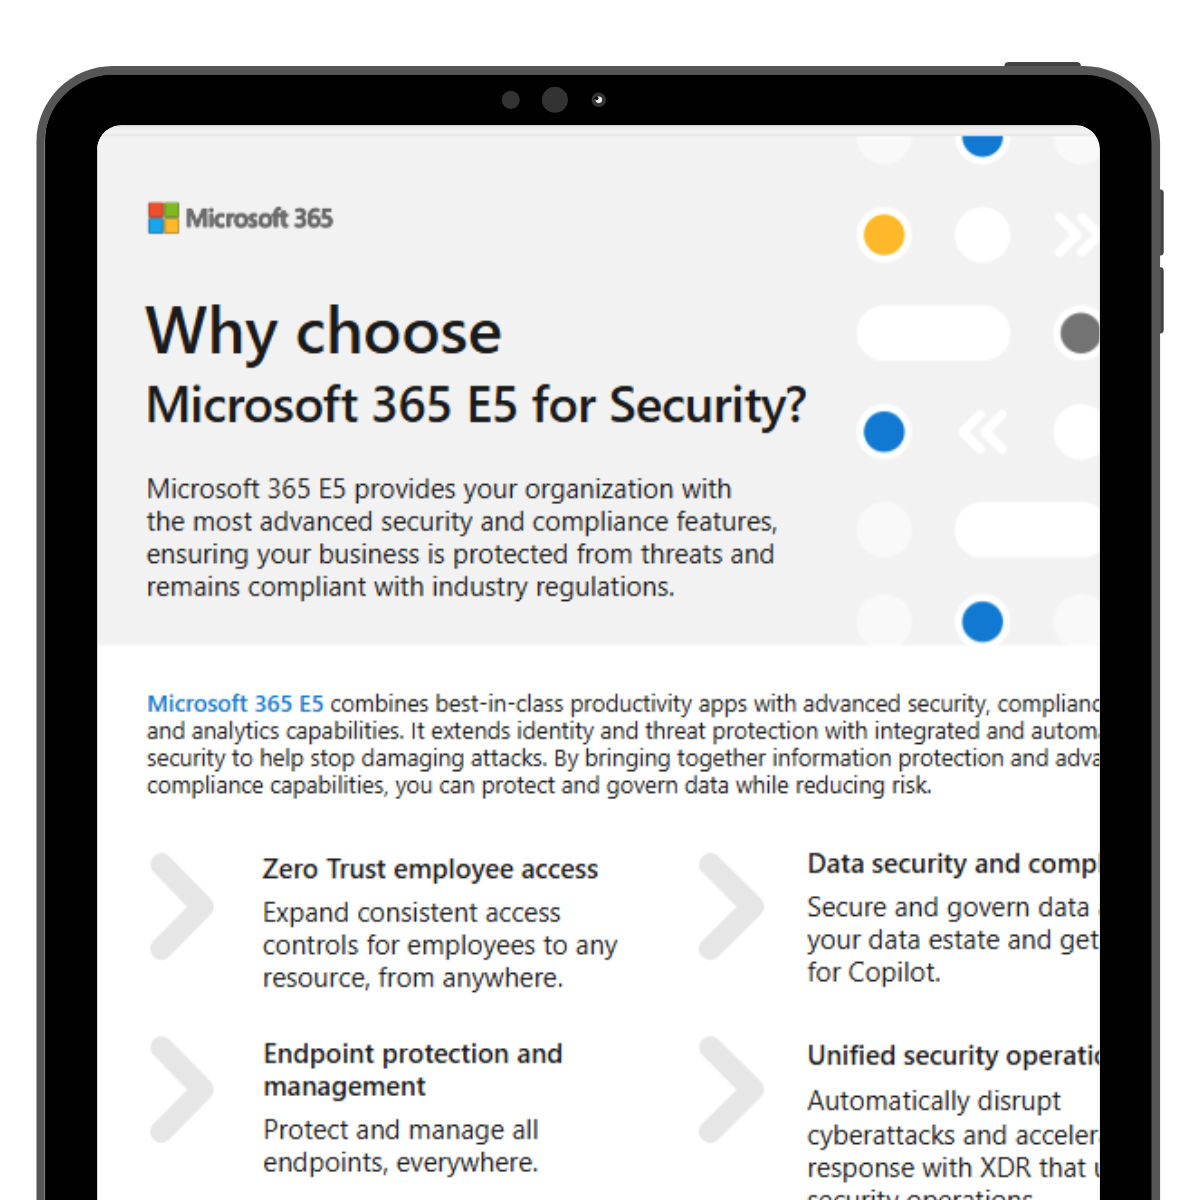
- Security workload management, such as Microsoft E5/E7, data loss prevention, and Advanced CTI
- Cross-platform alert correlation across Security Copilot and Microsoft security tools
- Continuous OT/ICS threat monitoring across plants and industrial controllers
- Full incident lifecycle management Threat hunting and analyst-led investigation
- Clear escalation procedures and executive and technical reporting
Whether you are moving workloads to Azure or addressing configuration and security gaps, Bulletproof gives you a clearer path forward. Understand where you are exposed and what should be addressed first.
- Microsoft 365 security posture reviews
- Threat protection assessment
- Data security assessments
- Security configuration validation
- Risk-prioritized remediation recommendations
- Penetration testing
- AI-readiness assessments/li>
Microsoft security tools provide maximum protection when connected across your entire digital environment. Contain threats faster and recover with greater confidence through managed detection and response (MDR).
- Alert investigation and validation
- AI data exposure, threat detection, and triage
- AI agent lifecycle control
- Incident containment guidance
- Root-cause analysis
- Incident response coordination
- Executive and stakeholder reporting
- Post-incident hardening recommendations
Explore Incident Response Services
You can’t govern or secure what you can’t see. Translate security technology into a practical, defensible security program.
- Microsoft security architecture guidance
- E5 security optimization and management
- Licensing and capability alignment
- Cloud application governance
- Identity and access recommendations
- Compliance and security framework alignment
- Emerging Microsoft technology advisory
- Security maturity and roadmap planning
OUTCOMES
Fewer Silos. Clearer Visibility. Cohesive Defense.
Gain after-hours coverage without the cost, complexity, and hiring challenges of building a 24/7 SOC internally.
Ensure that security controls remain aligned to your approved standards as your users, applications, devices, and cloud environment change.
We apply relevant threat information to your environment instead of delivering generic intelligence with no clear action.
We help create a repeatable response process so you can respond faster to cyberthreats.
Help employees recognize threats while giving leadership clear visibility into performance and risk trends.
Protect your organization with:
-
AI-ready monitoring
-
Alert triage
-
Secure AI adoption
-
Investigation across endpoints, identity, email, cloud applications, servers, networks and supported OT/ICS environments
Continuously strengthen your Microsoft security environment through:
-
Defender suite optimization
-
Policy baselines
-
Configuration monitoring
-
Drift Detection
Identify emerging threats before they become incidents through:
-
Curated cyber threat intelligence
-
Dark web monitoring
-
AI-enabled investigation
-
Human led, hypothesis-driven threat haunting
Reduce confusion when every minute matters with:
-
Automated SOAR playbooks
-
Structured escalation procedures
-
Incident containment guidance
-
Experienced analysts who understand your environment
Reduce preventable risk with:
-
Managed security awareness campaigns
-
Targeted training
Phishing simulations -
Continuous adoption of new Microsoft capabilities
-
Performance and cost tracked against business goals
-
A cycle of continuous improvement
Why Businesses Choose Bulletproof
“Bulletproof isn’t just another Microsoft vendor. They’re a true partner. Their team gives us personalized attention, works closely with our security experts, and adapts its approach to our needs and industry.”
“When we experienced a phishing incident, Microsoft Defender stopped it in its tracks and Bulletproof quickly assessed the situation. The malicious message was blocked and quarantined before it could do any harm.”
“Bulletproof understands our business and brings real expertise across IT, security, compliance, and Microsoft. Their team works alongside ours, adapts as our needs change, and helps us stay ahead in an evolving digital world.”
“Having one trusted partner across Managed IT, Managed Security, and Microsoft licensing has helped us simplify a complex environment, reduce costs, and improve IT efficiency by at least 20%.”
“Bulletproof’s flexible, white-glove MXDR service adapts to our environment and evolving security challenges, helping us stay ahead of threats and maintain compliance.”
“Bulletproof was on site and ready to support us with containment. They connected with our team immediately and worked side by side with us as if they were part of it.”
“Bulletproof isn’t just another Microsoft vendor. They’re a true partner. Their team gives us personalized attention, works closely with our security experts, and adapts its approach to our needs and industry.”
Trusted to Protect Organizations Around the Clock
Find Gaps in Your Threat Protection
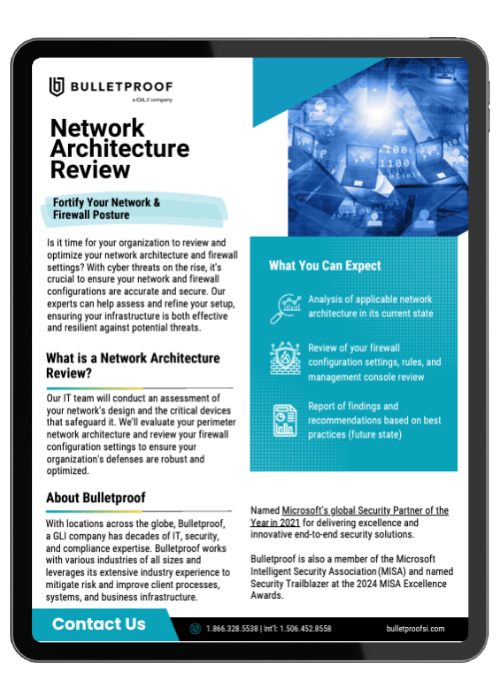
Get a comprehensive view of your current Microsoft security posture and identify the risks that require immediate attention.
CISO-Level Expertise Without the C-Suite Cost
A Virtual Chief Information Security Officer (vCISO) brings executive-level cybersecurity vision without the cost or commitment of hiring a full-time executive. Our vCISOs align your security governance with your core business objectives, building actionable short- and long-term roadmaps that connect daily IT decisions, compliance demands, and threat prevention.
The Bulletproof Experience
Instead of bolting on security as an afterthought, we align your Microsoft ecosystem, team workflows, and threat defense into one coordinated model that protects your people and adapts as you grow.
Take the Step Toward Stronger Security
RELATED RESOURCES
Resources to Strengthen Your Security Strategy
No results
Frequently Asked Questions
Learn how a managed security service provider can help your orga
A managed security service provider, or MSSP, helps organizations operate and improve their cybersecurity program.
The exact scope depends on the service level. Bulletproof Managed Security Services can include:
-
24/7 SOC monitoring
-
Alert triage and analyst-led investigation
-
Incident response and full lifecycle management
-
Microsoft Sentinel management
-
Microsoft Defender deployment and optimization
-
Configuration and drift detection
-
Cyber threat intelligence
-
Dark web monitoring
-
Detection and triage of AI-related alerts
-
Executive and technical reporting
-
Security assessments and strategic guidance
Add-ons could include:
-
Advanced threat hunting
-
Data security and managed data loss prevention (DLP)
-
Security awareness training
-
OT/ICS monitoring
-
Microsoft E5 and Microsoft E7 security optimization
An MSSP typically provides a broad range of outsourced security services, which may include monitoring, technology management, assessments, compliance, and consulting. Managed detection and response, or MDR, focuses more specifically on detection, investigation, and threat response. Extended detection and response, or XDR, correlates security information across multiple areas such as endpoints, identities, email, applications, and cloud workloads. Managed XDR, or MXDR, combines that broader technical visibility with 24/7 expert monitoring, investigation, threat hunting, and response.
=For most organizations, not entirely. An MSSP replaces the operational security function: 24/7 monitoring, alert triage, investigation, tooling management, and configuration oversight. What stays internal is ownership of risk decisions, business context, approval authority for changes, and the relationships an outside team can't have.
Generally, a small internal security function is required to set direction and make decisions, while an MSSP does the continuous operational work underneath it. If your organization has no internal security capability at all, you can pair managed services with a Virtual CISO to cover the governance and decision-making layer.
Outsourcing may be appropriate when your organization:
- Cannot provide 24/7 internal coverage
- Has difficulty hiring or retaining security analysts
- Is overwhelmed by alert volume
- Lacks Microsoft Sentinel or Defender expertise
- Needs to improve incident response readiness
- Must demonstrate security governance to executives or regulators
- Wants to reduce security vendor sprawl
- Needs to improve the return on its
- Microsoft investment
- Has experienced a breach or significant security incident
Close the Gaps in Your Security Coverage
Get 24/7 Microsoft-native managed security services and a clear plan for reducing risk without building and staffing an in-house SOC.