1 min read

Detect and disrupt in-progress cyberattacks automatically

Detect and disrupt in-progress cyberattacks automatically

Cybersecurity attacks are getting more common and targeted. They’re also accelerating; attacks that used to take months now take days. And even the most advanced security operations teams need to take breaks to keep their organizations protected. Our cyber security experts can help you stay ahead of evolving threats.

The Threats Are Real

  • Ransomware Attacks: Commodity and human-operated. <20 minutes from deployment to mitigate the attack.
  • Business Email Compromise (BEC) Attacks: Attackers pose as a trusted figure and ask recipients for payment or to share sensitive info. 81% between the first and second half of 2022.1
  • Adversary-in-the Middle (AitM): An unauthorized party intercepts communication between two systems or people. 100$ or less the cost of an AitM kit, which lowers the tooling and skills requires to launch an attack.2

1.Abnormal, “H1 2023: “Read “ Alert. 2023 | 2.Microsoft, “DEV-1101 enables high volume AiTM campaigns with open-source phishing kit,” March 13, 2023

Protect Your Business with Automatic Attack Disruption

What if you could detect and disrupt an in-progress attack automatically and dramatically reduce the overall impact? As a trusted technology partner with experience in security, we can help you get this capability with extended detection and response (XDR) from Microsoft.
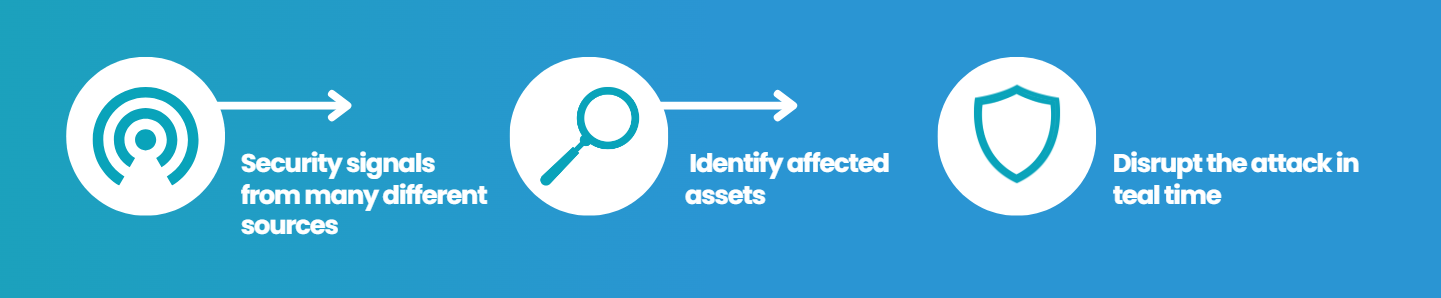
security signals,  identify affected assets, disrupt the attack.

Why we recommend Microsoft Defender XDR

Microsoft analyzes 65 trillion signals analyzed daily and correlates them in real time across attack surfaces.3 This threat intelligence powers automatic attack disruption in Microsoft Defender XDR.
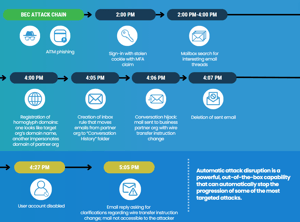
The Anatomy of a Real-Life BEC Attack

Microsoft 365 Defender used a combination of signals from identity and email security solutions—such as unfamiliar sign-in, inbox rule creation, and sending and deletion of emails—to identify the BEC attack and detect the fraud attempt.

Having established a high level of confidence through the combination of signals and alerts, Microsoft’s XDR automated actions then disabled the user account and disrupted the attack within three hours.

It prevented follow-up conversations and preventing the wire instructions from being acted upon.
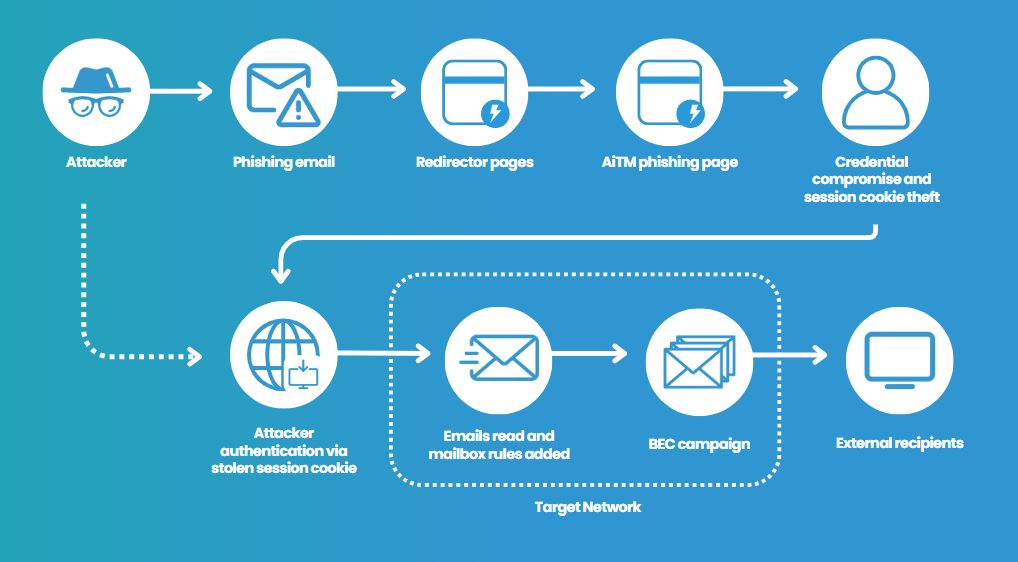
Automatic Disruption: AitM Attacks

The goal of automatic disruption is to contain the attack as early as possible.
  • Identify with high confidence an AiTM attack based on multiple correlated Microsoft 365 Defender signals.
  • Automatically disable the compromised user account.
  • Automatically revoke the stolen session cookie to prevent additional malicious activity.
  • Leave the SOC in full control of remediation.

Bulletproof Credentials

With 25+ years of IT, cybersecurity, and compliance experience, Bulletproof is a trusted Microsoft and Fortinet partner supporting organizations across North America. Our credentials include recognition on CRN’s 2026 Solution Provider 500, Fast Growth 150, and MSP 500 lists; Microsoft Security Trailblazer Award winner; 2021 Microsoft Global Security Partner of the Year; and 5× Microsoft Canada Security IMPACT Award winner. Bulletproof is also SOC 2 Type 2 compliant, a member of the Microsoft Intelligent Security Association, and a Fortinet Advanced Expert Partner, backed by 24/7 SOC, NOC, Service Desk, and Technology Operations capabilities.

Is Your Microsoft Environment Ready for Copilot and AI?

Is Your Microsoft Environment Ready for Copilot and AI?

Your employees already have new AI coworkers.
Read More
Securing Canada's Digital Communities: A Cybersecurity Roadmap for Municipalities

Securing Canada's Digital Communities: A Cybersecurity Roadmap for Municipalities

Security is no longer just about systems - it's about behavior
Read More
The Next Insider Threat Will Not Be Human

The Next Insider Threat Will Not Be Human

Author: Christopher Simm, CTO, Bulletproof

Read More